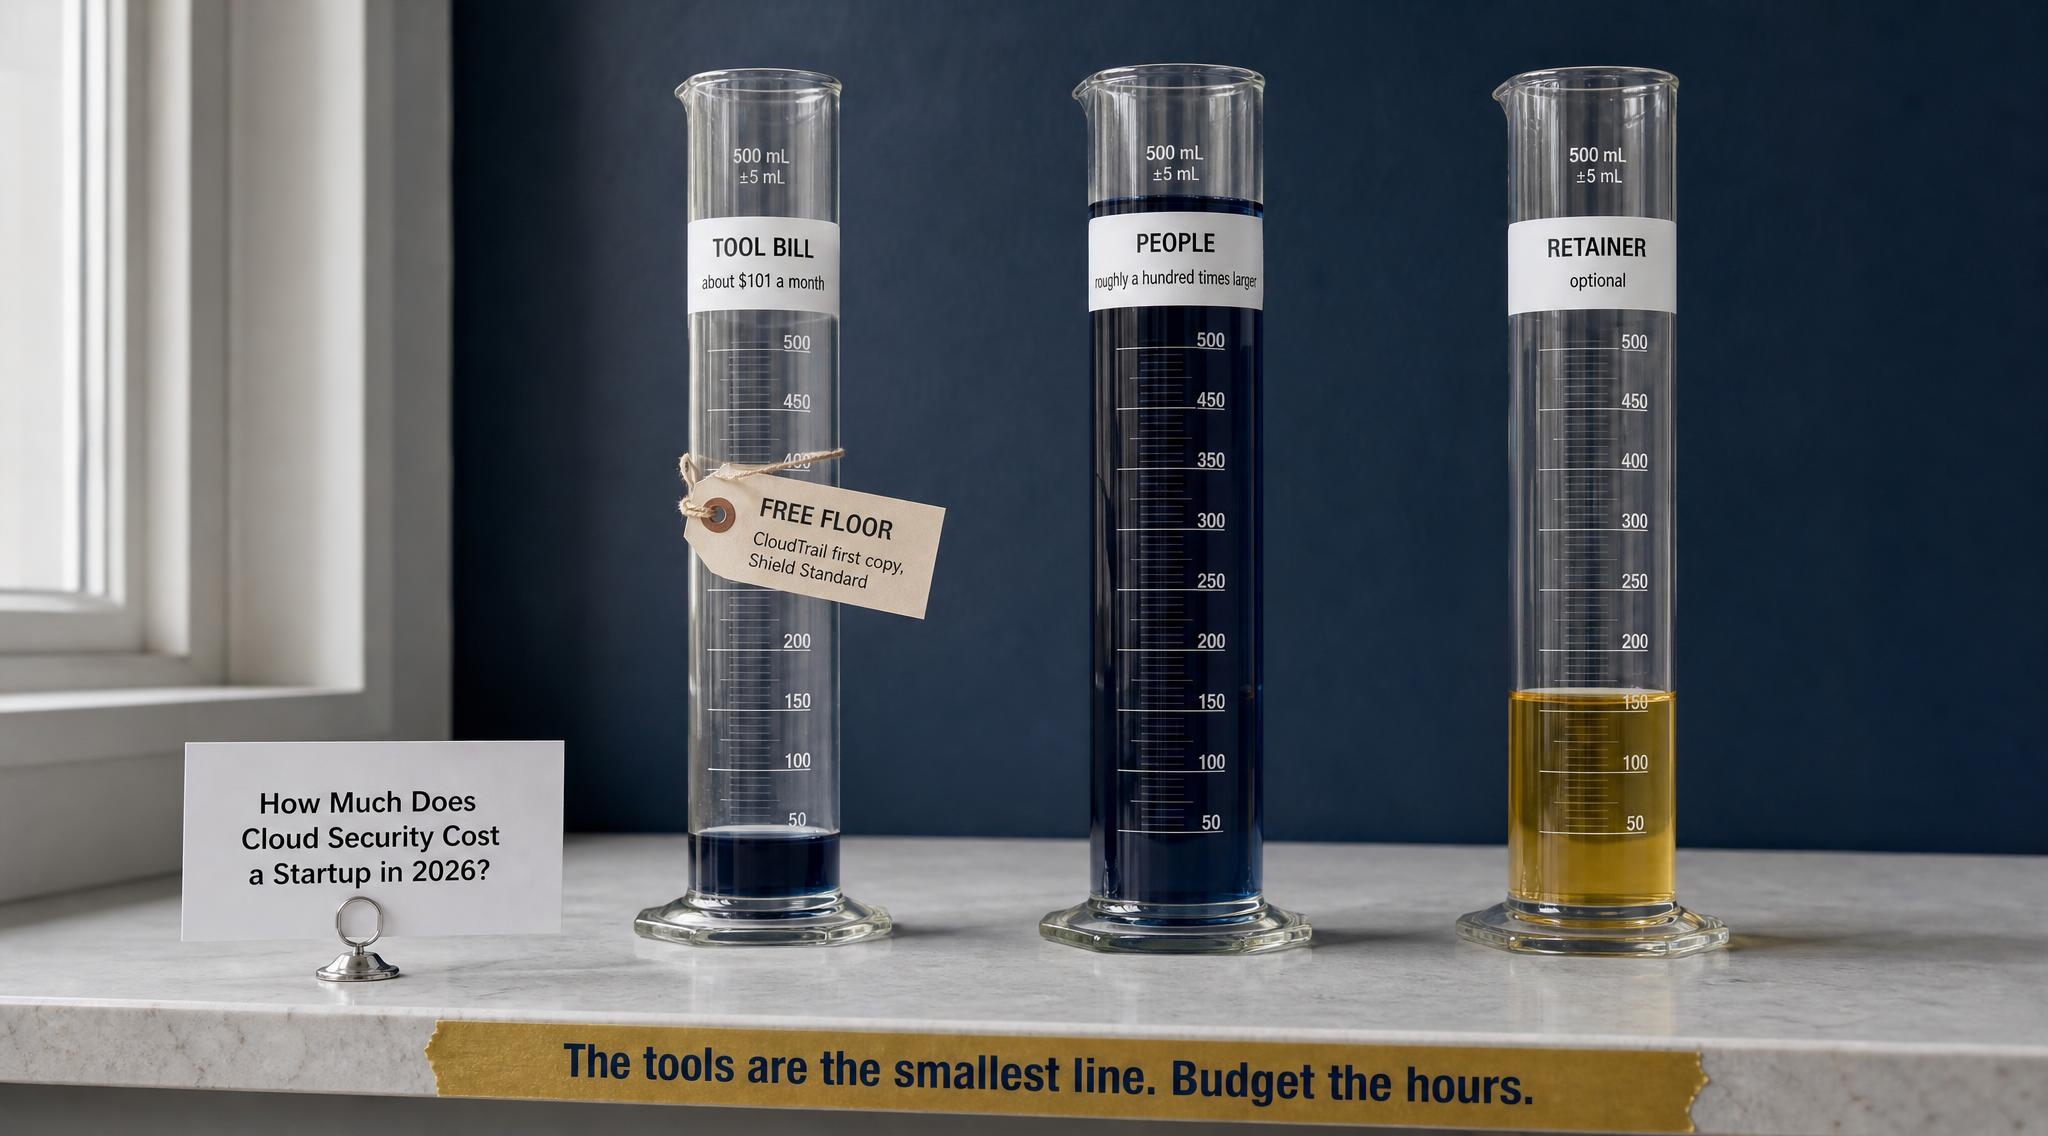
How much does cloud security cost a startup in 2026? For a team of 5 to 30 engineers on one cloud, cloud security cost comes in three lines: the native security tools your provider meters, the people who read and act on what those tools find, and, optionally, an outside team on retainer. The tool line is the smallest. On published list prices, one small AWS account can run its core detection, posture and identity checks for about $101 a month, before log volume (section 7 shows the arithmetic). The people line is roughly a hundred times larger.
This post is for the founder or first engineer asked "what will security cost us this year?". Provider pricing pages quote a fraction of a cent per check and leave you to guess the volume; industry articles quote enterprise breach figures in millions. Neither tells a small team what it will spend, and on what.
Three earlier posts go deeper on parts of this and are linked rather than repeated: how to secure an early stage AWS account covers which controls to switch on, what a DevOps or DevSecOps retainer costs in India covers the outside-team market, and virtual CISO services covers the leadership layer. Every price below is from the provider's own pricing page, linked inline, read in early November 2026, as US East (N. Virginia) list rates in US dollars unless stated.
Quick context: what changed in cloud security pricing going into 2026
Two things shape the bill now. First, the providers have pushed a real security floor down to zero. The first copy of CloudTrail management events, Shield Standard, IAM Access Analyzer's external access findings, Google Cloud's Security Command Center Standard tier and Microsoft Defender for Cloud's Foundational CSPM are all free.
Second, everything above the floor is metered by volume: events analysed, checks run, resources scanned, roles analysed, requests inspected. That means cloud security costs scale with the size and churn of your accounts, not with your headcount, and they scale per account and per region. The bill is predictable once you know which meter each service runs on.
What cloud security cost actually means
Cloud security cost is the total a company spends to keep its cloud accounts defended: the metered security services the provider bills, any third-party tools layered on top, and the human time to read, triage and fix what those tools find. It is not the same as the security line on your cloud invoice. The invoice is the visible part. The hours are usually the bigger part, and they never appear on the cloud bill at all.
1. The free floor: what costs nothing and should be on today
Start with what is free. AWS CloudTrail pricing delivers the first copy of management events in each region at no charge; additional copies cost $2.00 per 100,000 management events, and data events cost $0.10 per 100,000. One trail covering management events across regions is the audit log every later investigation depends on.
AWS Shield Standard protects against common network and transport layer DDoS events at no additional charge and is on automatically. IAM Access Analyzer external access analysis, which flags S3 buckets, roles and keys shared outside your account, also carries no additional charge, as does its policy generation.
The other two clouds do the same. Google lists the Security Command Center Standard tier as free of charge. Microsoft lists Defender for Cloud Foundational CSPM as free, covering continuous assessment, security recommendations and Secure Score across Azure, AWS and Google Cloud.
Practitioner opinion: the free floor takes an afternoon to enable, but free does not mean read. The takeaway is to switch all of it on this week and name one person to read each output.
2. Threat detection: GuardDuty bills on what it reads
The first paid line most AWS startups add is Amazon GuardDuty, the managed threat detection service. Its pricing page gives a 30-day free trial to accounts that have never enabled it, then bills by volume of what it analyses. CloudTrail management event analysis is $4.00 per million events, prorated, and AWS's own example of 40 million events in US East comes to $160 a month. VPC Flow Log and DNS query log analysis is billed per gigabyte, in tiers that get cheaper at higher volume.
One detail moves the number: GuardDuty does not charge for VPC Flow Log analysis from EC2 instances where its Runtime Monitoring agent is running, so runtime protection can shift cost between meters rather than simply adding.
The trial exists to give you a real number. AWS documents how to estimate GuardDuty usage cost from the console during the trial, broken down by data source. Read that estimate in week three, not after the first invoice.
Practitioner opinion: for a small account, GuardDuty is usually the best value line on the bill, because it turns the CloudTrail log you already collect into findings. Keep it.
3. Posture checks: Security Hub CSPM and the AWS Config line under it
Posture management answers "is anything misconfigured right now?" On AWS that is Security Hub CSPM. Its pricing page charges $0.0010 per security check for the first 100,000 checks per account per region per month, $0.0008 for the next 400,000, and $0.0005 above 500,000. Every account and region enabled gets a free trial first.
The line people miss is underneath it. Security Hub CSPM's checks depend on AWS Config, which is billed separately. AWS Config pricing is $0.003 per configuration item recorded in continuous mode, or $0.012 per item in periodic mode, and rule evaluations start at $0.001 each for the first 100,000 per region per month. A configuration item is recorded each time a resource changes, so a churning account records far more than a quiet one.
Both meters run per account and per region. Enabling posture checks in every region "to be safe" multiplies the bill by the number of regions while adding findings for regions you have nothing in.
Practitioner opinion: Config, not Security Hub CSPM, is the line that surprises small teams. Enable checks only in regions you run in, and consider periodic recording for resource types that churn.
4. Identity, keys and secrets: the per-unit lines
Three services bill per thing you own rather than per event, which makes them easy to forecast. IAM Access Analyzer's unused access analysis costs $0.20 per IAM role or user per month. Because IAM is global, one analyzer per account covers every region, and the AWS Security Blog advises creating only one per account, or one for the whole organization, to avoid paying twice.
AWS Secrets Manager charges $0.40 per secret per month plus $0.05 per 10,000 API calls, prorated by the hour, and rotation itself carries no charge beyond the Lambda that runs it. AWS KMS charges $1 per customer managed key per month and $0.03 per 10,000 requests, with a free tier of 20,000 requests a month across regions; AWS managed keys carry no monthly key fee.
These lines scale with architecture, not traffic. Practitioner opinion: a fast-rising role or secret count is a design smell before it is a billing problem, because every unused role is also an attack path. Count them once a quarter.
5. The edge and the scanners: WAF, Shield Advanced and Inspector
AWS WAF charges $5 per web ACL per month, $1 per rule per month and $0.60 per million requests inspected, with managed rule groups from AWS Marketplace sellers billed on top.
AWS Shield Advanced is a different purchase: $3,000 a month with a one-year commitment, plus data transfer fees. It adds application-layer DDoS response and cost protection. Practitioner opinion: it is not a seed-stage line; it earns its $36,000 annual commitment only when a DDoS outage would be a contractual or revenue event of that size.
Amazon Inspector scans for software vulnerabilities and bills per thing scanned: about $1.25 per EC2 instance per month for agent-based scanning in US East, about $0.09 per container image on its initial scan when pushed to ECR with $0.01 per rescan, and about $0.30 per Lambda function per month for standard scanning. New accounts get a 15-day free trial.
The takeaway: WAF in front of anything public, Inspector on whatever you actually run, and Shield Advanced only when you can name the business event it insures against.
6. Google Cloud and Azure: the same bill under different names
The structure repeats on the other two providers: a free posture tier, then paid tiers billed per resource. On Google Cloud, Security Command Center Standard is free; Premium is sold as a fixed subscription or pay-as-you-go. Pay-as-you-go charges at project level are based on the usage of specific resources in that project, and from 1 January 2026 Cloud Run and AlloyDB are each billed at $0.0071 per vCPU-hour for project-level activations.
On Azure, Defender for Cloud keeps Foundational CSPM free and charges for Defender CSPM and the workload plans. Defender for Servers comes as Plan 1 and Plan 2, priced per server per month on Microsoft's regional pricing page; third-party summaries commonly cite figures near $5 and $15, so confirm the live number for your region before budgeting.
A comparison rule that holds across all three: the free tier tells you what is misconfigured, and the paid tier adds threat detection, vulnerability scanning and deeper workload coverage, billed per resource. Switching providers does not make security cheaper; the meters have different names and the same shape.
7. A worked tool bill for one small AWS account
Here is the arithmetic, using the list prices above. This is a hypothetical account, not a quote and not an engagement: one AWS account, one region (US East), 5 million management events a month, 10,000 Security Hub CSPM checks, 5,000 configuration items and 10,000 Config rule evaluations, 30 IAM roles and users, 10 secrets, 3 customer managed KMS keys inside the free request tier, one web ACL with 5 rules and 10 million requests, and Inspector on 10 EC2 instances and 50 image pushes. It ignores free trials and free tiers, so it slightly overstates a first month.
| Line | Volume (assumed) | List rate | Monthly |
|---|
| CloudTrail, first management copy | All regions | Free | $0 |
| GuardDuty, CloudTrail analysis | 5 million events | $4.00 per million | $20.00 |
| Security Hub CSPM checks | 10,000 checks | $0.0010 per check | $10.00 |
| AWS Config, configuration items | 5,000 items | $0.003 per item | $15.00 |
| AWS Config, rule evaluations | 10,000 evaluations | $0.001 each | $10.00 |
| Access Analyzer, unused access | 30 roles and users | $0.20 each | $6.00 |
| Secrets Manager | 10 secrets | $0.40 each | $4.00 |
| KMS customer managed keys | 3 keys | $1 each | $3.00 |
| WAF | 1 ACL, 5 rules, 10 million requests | $5 + $1 per rule + $0.60 per million | $16.00 |
| Inspector, EC2 | 10 instances | about $1.25 each | $12.50 |
| Inspector, ECR images | 50 initial scans | about $0.09 each | $4.50 |
| Shield Standard | Automatic | Free | $0 |
| Total, before GuardDuty log volume | | | about $101 a month |
The volumes are assumptions; your real ones come from Cost Explorer after the trials end. Change them and the total moves, but at this size the order of magnitude is tens to low hundreds of dollars a month, not thousands.
8. The people line: the cost that never appears on the cloud bill
Every tool above produces findings, and none of them fixes anything. Someone has to read each finding, decide whether it is real, and change the infrastructure, and that person's time is the largest line in cloud security cost by far.
For a reference point, the US Bureau of Labor Statistics reports a median annual wage of $124,910 for information security analysts in May 2024, before benefits. That is about $10,400 a month in salary alone, roughly a hundred times the worked tool bill above. Salaries in India are lower in absolute terms and the gap is still wide; the hire versus MatrixGard comparison and the retainer cost post lay out the India numbers rather than restating them here.
Practitioner opinion: most startups under 30 engineers do not hire a dedicated security person and spend engineer hours instead, usually uncounted. A small account with the stack above needs a few hours a week of competent review, plus fix time that spikes after every architecture change, and those hours come out of product work.
The takeaway: put the hours in the budget, name the person, and treat unread findings as cost with no security bought.
9. A retainer line, and what it does and does not replace
The third line is optional: an outside team that owns the reading and fixing. Disclosure first: MatrixGard sells exactly this, a fractional DevSecOps retainer covering cloud, DevOps and security together, so weigh this section with that in mind. Our published pricing page lists the retainer as Starter $2,500 a month for international clients, or ₹30,000 a month in India, for up to 20 hours a month plus async support. A one-time Full Audit is $1,500, or ₹15,000 in India, and the first audit call is free.
Two things a retainer never replaces. It does not replace the cloud bill: every tool in sections 1 to 6 is still billed by the provider to your account. And it does not replace an attestation: a SOC 2 report is issued only by a licensed CPA firm, engaged and paid separately, which the SOC 2 cost post covers.
What it replaces is the unbudgeted hours in section 8, and the hire you are not ready to make. The decision rule: if someone on your team has the skill and the hours to read the findings every week and fix them, a retainer is not the right buy; keep the money and the knowledge in house. If nobody does, and you would otherwise leave findings unread, a retainer is cheaper than a hire and cheaper than the incident. Before signing with any provider, including us, read how to verify a fractional DevSecOps consultant.
The takeaway: price a retainer against the hours it removes, never against the tool bill.
10. The cost of spending nothing
The last line is the one with no invoice. IBM's Cost of a Data Breach Report 2025 puts the global average cost of a breach at $4.44 million. For India, IBM's India release reports a record average of INR 220 million, about ₹22 crore, up 13 percent on the year. Both samples skew toward larger organizations, so read them as the direction of risk, not as the price a 10-person startup would pay.
For Indian startups, regulation adds fixed obligations. The CERT-In directions of 28 April 2022 require listed cyber incidents to be reported within six hours of noticing them, which is hard to meet without the logging in section 1. The Schedule to the Digital Personal Data Protection Act, 2023 sets a penalty of up to ₹250 crore for failure to take reasonable security safeguards to prevent a personal data breach under section 8(5); the DPDP Act post covers what the Act asks of a startup.
The takeaway: the do-nothing number is not a price you can budget; it is the reason the floor is the first thing to switch on.
Summary table
| Line | What it covers | Published price | Scales with |
|---|
| Free floor | CloudTrail first copy, Shield Standard, Access Analyzer external access, SCC Standard, Foundational CSPM | Free | Nothing |
| Threat detection | GuardDuty | $4.00 per million CloudTrail events, plus per GB logs | Activity and log volume |
| Posture checks | Security Hub CSPM plus AWS Config | $0.0010 per check; $0.003 per configuration item | Resources, churn, accounts and regions |
| Identity and secrets | Access Analyzer unused access, Secrets Manager, KMS | $0.20 per role or user; $0.40 per secret; $1 per key | Architecture |
| Edge and scanning | WAF, Inspector, Shield Advanced | $5 per ACL; about $1.25 per instance; $3,000 a month | Public endpoints and workloads |
| People | Reading and fixing findings | $124,910 US median salary (BLS) | Findings and change rate |
| Retainer (optional) | Outside team owns the reading and fixing | Starter $2,500 a month, or ₹30,000 in India | Scope and hours |
Prices are from the provider and BLS pages linked above; the scaling column is practitioner opinion. The tools are the smallest line. Budget the hours.
What to spend at your stage (practitioner opinion)
Pre-seed, one to five engineers. The free floor plus GuardDuty after its trial. One person, one hour a week, reading findings. Tool spend should be tens of dollars a month.
Seed, five to twenty engineers. Add Security Hub CSPM in the regions you use, Access Analyzer unused access, WAF in front of anything public and Inspector on what you run. Budget a few named hours a week, or a retainer if nobody owns them.
Series A, or the first enterprise customer. Multi-account, organization-wide analyzers, and a real answer for the security questionnaire. This is where a first security hire or a larger retainer scope starts to make sense.
Whatever stage you are at, start by seeing where your account stands today: open the free security checklist.
Avinash S is the founder of MatrixGard. Fractional DevSecOps for early-stage startups, funded or bootstrapped across India, the GCC, the UK, and the US. Almost a decade of building, breaking, and securing cloud infrastructure for fintech, healthtech, and SaaS workloads.
Methodology note. This post answers what cloud security costs a small startup as a set of budget lines, and does not cite any engagement of ours. Tool prices are from the AWS, Google Cloud and Microsoft pricing pages linked inline, read in early November 2026, as US East (N. Virginia) list rates in US dollars; rates vary by region and change, so check the live page before buying. Salary and breach figures are from BLS and IBM, linked inline. The worked bill in section 7 is hypothetical arithmetic on list prices with stated volumes. The review hours, the stage advice and the decision rules are practitioner opinion. No client outcome, testimonial or price other than MatrixGard's published one appears in this post.