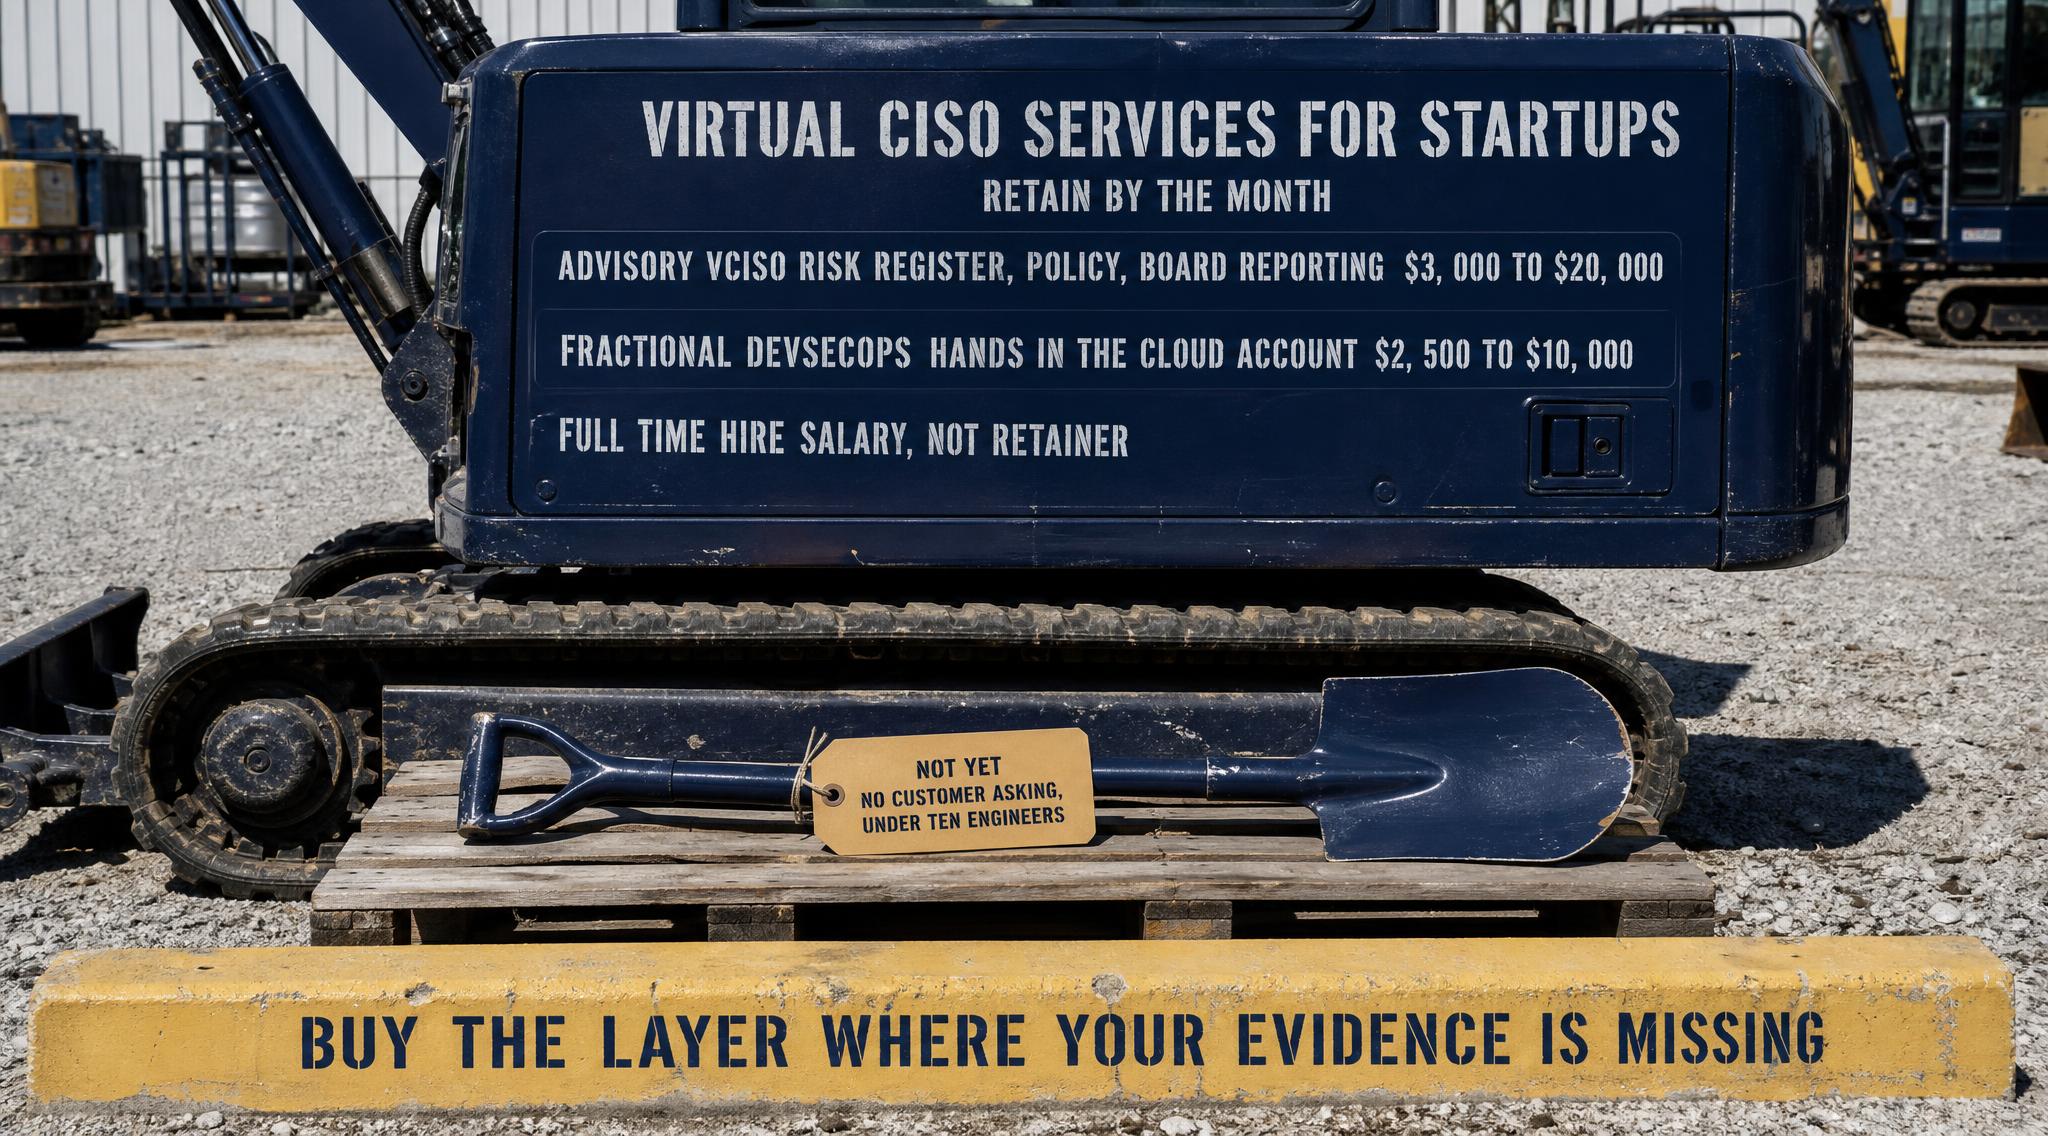
Search virtual CISO services for startups and you get two different products wearing one label. One is an advisory retainer: a security leader who joins your calls, writes the policy set, answers the enterprise questionnaire and signs their name next to your risk decisions. The other is a delivery retainer: people who go into your cloud account and change things. Both get sold as a vCISO, and the shorter query, vciso for startups, returns the same split under a shorter name. They cost different money and they fix different problems.
This post is for a founder or an engineering lead at a company of five to fifty people who has just been told, usually by a customer or an investor, that they need someone accountable for security. It covers what the engagement includes, what it costs per month against published numbers, and the case where the honest answer is that the money buys more somewhere else this quarter.
What most articles on this get wrong is the last part. They are written by providers, so every reader turns out to need one. The qualify-out is the section that makes the rest of it worth reading.
Virtual CISO services for startups, defined
A virtual CISO is a security leader you retain by the month instead of employing. Virtual CISO services for startups usually cover the executive layer of a security programme: risk decisions, policy, audit readiness, vendor review, incident command and a named person who is accountable to your board for all of it. The work is governance rather than engineering. A vCISO decides, documents and defends the decision; changing the IAM policy is still somebody else's afternoon.
That distinction is the whole basis on which you should judge a quote. If a proposal promises both the governance layer and the hands in the console for one small monthly fee, ask which one gets dropped in a busy month. The answer is always the hands.
Why the role is sold so hard in 2026
Three things happened at once, and none of them are marketing.
First, governance became an explicit control. The NIST Cybersecurity Framework 2.0 added GOVERN as a function of its own, with a category (GV.RR) that asks for cybersecurity roles, responsibilities and authorities to be established, communicated, understood and enforced. A framework that used to describe controls now asks who owns them.
Second, the public-company rules made the question routine. The SEC cybersecurity disclosure rules require registrants to describe management's role in assessing and managing material cyber risk, including which positions hold it and what expertise they have. Your enterprise customer answers that question every year, and the easiest way for them to answer it is to push the same question down to you.
Third, the questionnaire got harder. A vendor security review that used to be twelve questions now runs to a spreadsheet, and several rows ask for a named security owner rather than a control. We wrote about that specific gauntlet in the security questionnaire your enterprise buyer just sent.
What the engagement actually covers
A serious vCISO retainer is a programme, not a set of calls. Across published scopes the same eight items recur, and this is the list to hold any proposal against.
- A risk assessment that produces a ranked register, not a PDF of generic threats.
- A policy set written for your actual stack, with review dates that someone owns.
- Questionnaire and audit response: SOC 2, ISO 27001, customer security reviews.
- Vendor and subprocessor review, including the AI tools your team signed up for last quarter.
- Access governance: joiner, mover, leaver, and a quarterly review with evidence.
- Incident response ownership: the plan, the tabletop, and the phone call at 02:00.
- Board and investor reporting in language a non-technical director can act on.
- A roadmap with named owners and dates, reviewed monthly against what shipped.
The takeaway: if a proposal cannot tell you which of these eight are in scope and which are extra, it is priced on hours rather than outcomes, and you will find that out in month three.
vCISO, fractional DevSecOps or a full time hire
This is the comparison the pricing pages avoid, because the three products overlap in the brochure and almost never overlap in practice.
A vCISO gives you accountability, documentation and the buyer-facing answer. A fractional DevSecOps retainer gives you hands in the cloud account: the logging that was never turned on, the IAM policy that grants star, the backups nobody has restored. A full time hire gives you both, at a salary, once there is enough work to fill a week.
The decision rule that holds up: buy the layer where your evidence is missing. If your controls are broadly in place and you cannot describe them to a buyer, you have a governance gap and a vCISO closes it. If you can describe them and the description is optimistic, you have an engineering gap and advice will not close it. If both are true and the backlog is more than about two days of work a week, you are hiring, and the retainer is a bridge until the hire lands.
What virtual CISO services for startups cost per month
Published numbers first, because most providers do not print one. SideChannel's pricing guide puts the market at 3,000 to 20,000 US dollars a month. Atlant Security publishes a range of 3,500 to 15,000 US dollars a month for 2026. Both bands describe the same shape: a small monthly commitment of senior hours at the bottom, a full compliance programme with audit management at the top.
For contrast, a fractional DevSecOps retainer is priced on the same axis and lands lower, because the seniority premium of a board-facing title is not in it. MatrixGard publishes its retainers openly rather than quoting on request: Starter at $2,500/mo, Growth at $5,000/mo, Scale at $10,000/mo, with an India-market price of ₹30,000 for Starter. Those are hands-on engineering retainers, not board advisory, which is exactly the distinction this post is about. The full ladder is in the DevSecOps retainer cost breakdown.
The practical read: below roughly three thousand dollars a month, nobody is running a full governance programme for you. They are giving you a few hours of senior attention and a template library. That can be the right purchase. Just buy it knowing which one it is.
What moves the price
Four variables account for most of the spread between a three thousand dollar retainer and a fifteen thousand dollar one.
Committed hours. Almost every provider prices a band of senior hours per month. Ask for the number and ask what happens when a month runs over it.
Regulatory load. A payments or health or defence context adds evidence work that has nothing to do with your engineering. PCI DSS, HIPAA and CMMC scopes are consistently quoted higher across the published guides.
Audit ownership. There is a real difference between a vCISO who prepares you for the audit and one who runs the audit relationship, handles the auditor's follow-ups and owns the remediation plan.
Incident command. Whether the retainer includes being on the phone during an incident, and on what response time, is the single item most likely to be missing from a cheap quote. Ask for it in writing.
Takeaway: the four questions above turn an opaque monthly figure into a comparable one, and they take one email to ask.
The compliance triggers that genuinely create the need
Most teams buy this role because a specific document demanded it, and it is worth knowing which documents actually do.
PCI DSS is the most explicit. Requirement 12.1.4 of PCI DSS v4.0.1 assigns responsibility for information security formally to a chief information security officer or another knowledgeable member of executive management. If you touch cardholder data, a named accountable executive is not optional. The standard is published in the PCI Security Standards Council document library.
ISO/IEC 27001 works differently. Clause 5.3 of ISO/IEC 27001:2022 requires top management to assign and communicate the responsibilities and authorities for information security roles, including reporting on the management system's performance. It requires the role to exist and be assigned. It never says the person has to be on your payroll, which is the clause that makes a vCISO an auditable answer.
SOC 2 has no equivalent hard clause, but the control environment criteria ask you to show structure, authority and responsibility, and an auditor reads an empty org chart the way you would expect. Cost and timeline for an Indian team are in the SOC 2 India cost breakdown.
India's DPDP Act creates a different role, and conflating the two is a common and expensive mistake. Section 10 of the Digital Personal Data Protection Act, 2023 requires a Significant Data Fiduciary, once notified as one by the Central Government, to appoint a Data Protection Officer who is based in India and answerable to the board. That is a privacy role with a residency condition, not a security role, and a vCISO in another timezone does not satisfy it. Our DPDP compliance guide covers the wider obligation set.
What the retainer does not include, and who does that work
Read any vCISO scope closely and the verbs are decide, define, review, report and advise. The verbs that are missing are configure, migrate, patch and restore. That gap is the source of nearly every disappointed renewal conversation in this market.
So plan for it from the start. The engineering work behind a control still needs an owner, and there are three honest ways to cover it: your own engineers take it with the vCISO setting the standard, the same provider sells a separate delivery retainer, or you bring in a second party for the hands. Any of the three works. What does not work is assuming it was included because the proposal mentioned the control.
Takeaway: before you sign, take the top five items on the risk register and ask, out loud, who types the fix. If the answer is a name on your side, make sure that person has the hours.
When you are too early, and what to do instead
There is a point below which this purchase buys you a document set and a false sense of progress, and it is more common than the vendor pages suggest. The honest signals that you are early: no customer has asked for a security review, you are not in a regulated data class, you have fewer than about ten engineers, and nobody has yet turned on the controls a provider would immediately ask about. That last one is the real test. A governance layer over an ungoverned estate produces a very good description of your gaps.
What to do instead this quarter, in order, and all of it is inside a small team's own capability. CISA's Cyber Essentials frames the same starting set for small organisations, with leadership as the first element rather than the last.
- Enforce multi-factor authentication on the identity provider, the cloud root accounts and the code host, with no exceptions carved out for founders.
- Turn on audit logging in the cloud account and send it somewhere the account itself cannot delete.
- Restore one backup end to end and write down how long it took. An untested backup is a plan, not a control.
- Remove standing administrative access for anyone who does not need it this week, and diary a quarterly review.
- Write a one-page incident plan naming who declares, who calls the customer and who talks to the regulator.
Practitioner opinion, stated as such: those five, done properly, answer more questionnaire rows than a policy library does, and they make the vCISO engagement cheaper when you do buy one, because the first ninety days of a retainer usually go on exactly this list.
How to shortlist a provider in three checks
These three separate the real practices from the resellers quickly, and none of them need a call.
Check one: does the site say what the deliverables are, month by month? A practice that runs programmes can describe the first ninety days without a discovery call. One that cannot is selling availability.
Check two: who is the named person, and what else are they doing? Ask how many companies that individual covers. There is no correct answer, but a provider that will not tell you is answering anyway.
Check three: is there a price anywhere? Most of this market quotes on request. We checked the India-facing providers for a related post and found the same pattern, written up in the vCISO provider review. A published price is not proof of quality, but it is proof that the scope is fixed enough to have one.
The summary table
| Option | What you get | Published monthly range | Best when |
|---|
| Advisory vCISO | Risk register, policy, questionnaire answers, board reporting | $3,000 to $20,000 | Controls exist, the evidence does not |
| Fractional DevSecOps | Hands in the cloud account, fixes and automation | $2,500 to $10,000 | The description of your controls is optimistic |
| Both, from one provider | Governance plus delivery, one accountable party | Top of both bands | An audit date is fixed and close |
| Full time hire | Everything, on your payroll | Salary, not retainer | More than two days of work a week |
| Not yet | The five controls listed above, done in house | Your own time | No customer asking, under ten engineers |
Stage by stage: pre-seed, seed, Series A
Pre-seed. Almost always the last row of that table. Put the five controls in place, keep the receipts, and revisit when a deal needs a security review. The exception is a regulated data class from day one, where the requirement arrives with your first customer rather than your tenth.
Seed. This is where the trigger usually lands: an enterprise pilot, an investor's diligence pack or a SOC 2 commitment made in a sales call. Buy the layer you are missing rather than the title. Most seed teams at this point have a governance gap and a smaller engineering gap than they fear.
Series A. The programme now outlives any single engagement, and the question shifts from whether to retain a vCISO to when the first internal security hire lands. A retainer that is not visibly building toward that handover is being renewed out of habit.
Where MatrixGard fits, and where it does not
Disclosure, because this is my own practice: MatrixGard is a fractional DevSecOps retainer, which is the second row of the table, not the first. The work is cloud, infrastructure and security engineering for early-stage teams, funded or bootstrapped, at the published prices above.
Where it does not fit: if what you need is a board-facing security executive to own the governance programme and carry the title into audit meetings, a dedicated vCISO practice is the better purchase, and several of them publish their scope clearly. If what you need is somebody to turn on the logging, fix the access model and then help you answer the questionnaire honestly, that is the retainer.
If you want a second opinion
If you are weighing this decision right now, the fastest way to find out which gap you actually have is to look at the controls rather than the org chart. There is a free checklist on the MatrixGard site that walks the same ground a provider would cover in a first call: identity, logging, backups, access and incident readiness. Work through it, and the answer to the vCISO question usually settles itself. If it does not, a twenty-minute conversation costs nothing and there is no obligation attached to it.
About the author
Avinash S is the founder of MatrixGard, a fractional DevSecOps practice working with early-stage startups on cloud, infrastructure and security. He writes about the engineering decisions behind compliance, cloud cost and security posture for teams without a dedicated security function.
Methodology and sources
Pricing bands in this post are quoted from published vendor pricing guides and linked to the page that publishes them: SideChannel and Atlant Security. MatrixGard's own prices are the ones published on its pricing page and are stated here in full rather than as a range. Regulatory statements are taken from primary texts: PCI DSS v4.0.1 from the PCI Security Standards Council document library, ISO/IEC 27001:2022 clause 5.3 from the standard's own page, the Digital Personal Data Protection Act, 2023 from the MeitY publication, the NIST Cybersecurity Framework 2.0 from NIST, and the SEC cybersecurity disclosure rules from the SEC's own release and its small business compliance guide. No client outcome, engagement figure or testimonial appears anywhere in this post, and the sections marked as practitioner opinion are judgement rather than measurement. Published 24 September 2026.